Spy Planes, Signal Jammers, and High-Tech Weapons in Syria

The relationship between Russia and the West is becoming increasingly dangerous with potential flashpoints developing in both eastern Europe and Syria. After repeated incursions into Turkish airspace by Russian warplanes on bombing raids over Syria, NATO’s secretary general Jens Stoltenberg warned Moscow that it stands ready to “defend all allies”. In the meantime Britain announced it will ship troops to Baltic states to defend NATO’s eastern boundaries against potential Russian aggression beyond Ukraine.

 The Krasukha-4 is a broad-band multi-functional jamming system designed to neutralize Low-Earth Orbit (LEO) spy satellites such as the US Lacrosse/Onyx series, airborne surveillance radars and radar-guided ordinance at ranges between 150km to 300km. The system is reported to have the ability to cause damage to the enemy’s EW systems and communications. The Krasukha-4 system works by creating highly effective jamming at the fundamental radar frequencies and different radio-emitting sources.

In recent weeks, Russia has also deployed the IL-20 surveillance plane, better recognized by its NATO title “Coot” and roughly equal to the U.S. Navy’s P-3 Orion, a mainstay of the Pentagon’s spy tools. The Russian aircraft is bristling with high-tech equipment like surveillance radar, electronic eavesdropping gear, and optical and infrared sensors. One of the Kremlin’s premier spy planes, it offers Russian forces with a powerful tool for finding rebel units and assigning targets to its fighter planes. In late September, Syrian rebels posted a video purporting to show the aircraft flying over a battlefield.

https://www.youtube.com/watch?v=9qwNY9GFXp8

The deployment of the IL-20, or Coot, is probably the clearest indication that Russian President Vladimir Putin wants to ensure his troops in Syria aren’t reliant on Assad’s forces for targeting info — and that they could be getting ready for a ground combat position. On Monday, Moscow said “volunteer” troops could be heading to Syria to join the battle there, a barely disguised sign that Russian forces might soon be directly battling U.S.-backed and trained rebels inside Syria.
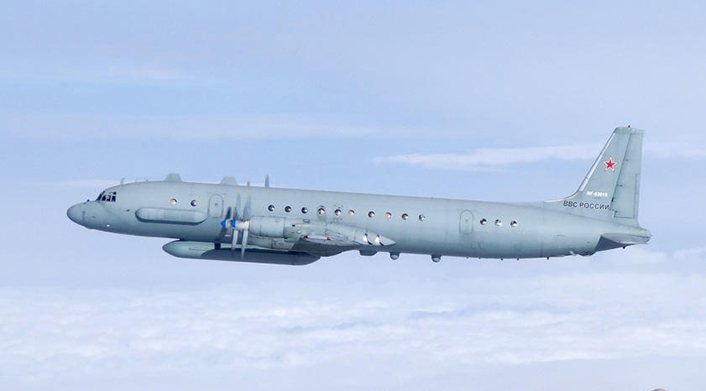
Coot or IL-20
The ‘Coot’ or the Ilyushin Il-20 (IL-20) – Source: theaviationist.com

Russia’s transfer of advanced electronic warfare tools to Syria is the latest instance of Moscow’s so-called “hybrid warfare” tactics, which use deception and covert operations to achieve strategic objectives with a minimal use of military force. The Krasukha-4 was also noticed in Ukraine and played a key part in Russia’s campaign of electric warfare there, which Kiev claimed resulted in a disruption of cell service at times. The deployment of the Krasukha, which can be utilized to disable aircraft avionics, came at around the same time that Western policymakers publicly entertained the idea of creating a no-fly zone over eastern Ukraine. The positioning of the Krasukha, along with other air defenses, prevented the enforcement of such a no-fly zone and kept Kremlin in charge of the skies, according to Igor Sutyagin, a senior research fellow at the Royal United Services Institute, a London based think tank.

Now, too, the Krasukha has been put in place as several countries are calling for the establishment of a no-fly zone in northern Syria. Sutyagin described the deployment of the Krasukha as an effective “no-fly zone for those who wish to create a no-fly zone.” For now, there isn’t any proof that the electronic warfare system has been used against American and other coalition planes flying in the skies over Syria, however its presence has surely been noted by the Americans.

The usage of cutting-edge signals intelligence and electronic warfare tools is indicative of Russian intentions in Syria. Jeffrey White, a fellow at the Washington Institute for Near East Policy and a 34-year veteran of the U.S. Defense Intelligence Agency, described the rebels as not “that hard a SIGINT target,” utilizing a shorthand term for signals intelligence, or transmissions plucked off the airwaves. “Do [the Russians] want their best and most sophisticated collection techniques and methods?”

Russia’s use of the new tools — particularly the equipment designed to provide more precise targeting data — comes amid a fierce debate between Russian and the American administration over Russia’s true targets in its Syria air war. Russian leaders insist they’re only hitting targets tied to the Islamic State, however rebel groups in the country — backed by senior U.S. officers like Defense Secretary Ash Carter — say Moscow is actually dropping virtually all of its ordnance in areas held by groups combating Assad.

Russia and Syria have a long history of intelligence cooperation in the fight against the country’s rebels, and Russia has previously provided alerts intelligence expertise to the Syrian authorities. In October 2014, rebels overran a Syrian military base close to the Golan Heights, discovered a joint Russian-Syrian listening post, and posted a video tour of the secretive facility.

Asked in regards to the intensified Russian intelligence buildup in Syria, one U.S. senior defense official remained closed-lipped about Moscow’s capabilities there apart from acknowledging the sophisticated instruments at Russian troops’ disposal and that “their operational patterns remain the same” as in Ukraine. Speaking on condition of anonymity to discuss classified details, the official stated that Russia has concealed communications and movements as it did in Ukraine, including by hiding Russian fighter jets within the signature of larger cargo jets.
R-166-0.5
R-166-0.5 Signals Vehicle

Other assets deployed to Syria include the R-166-0.5 signals vehicle, which provides command and control functions for a battalion of Russian ground troops. Its presence in Syria is intriguing, Sutyagin stated, because it implies the presence of a battalion-strength detachment of ground troops. On Monday, Interfax reported that the Vasily Tatishchev, an advanced naval surveillance ship, has sailed for the eastern Mediterranean.
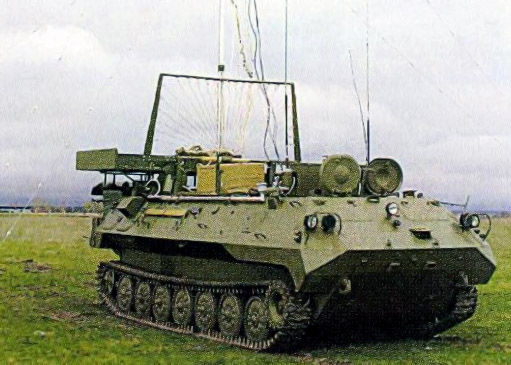
R-330P
The R-330P

Earlier this summer, military blogs reported that the Syrian military had obtained from Russia a brand new batch of R-330P communication jammers. The simple radio communications tools utilized by anti-Assad rebels are simple fodder for such a system and could be used to undermine coordination by insurgent forces in mounting operations and offensives.

Between the Krasukha, the IL-20, and the Vasily Tatishchev — along with the reported presence of surveillance drones — Russia has poured its best assets into Syria against targets that really shouldn’t be particularly hard for the country’s air force to hit. However that deployment is still quite small, and its concentrated use has allowed Putin to achieve his objectives with a minimal amount of effort.

Hi-Tech All The Way

Since the starting of the Arab Spring, NATO countries led by the US and directly supported by the UK have been actively gathering intelligence from countries using EW assets together with low-orbit surveillance satellites (Lacrosse/Onyx series), reconnaissance planes (NATO E3 Sentry (AWACS), USAF RC135-Rivet Joint, RAF’s Sentinel R1 and Reaper drones), and sharing intelligence data with the side being supported in the battle.
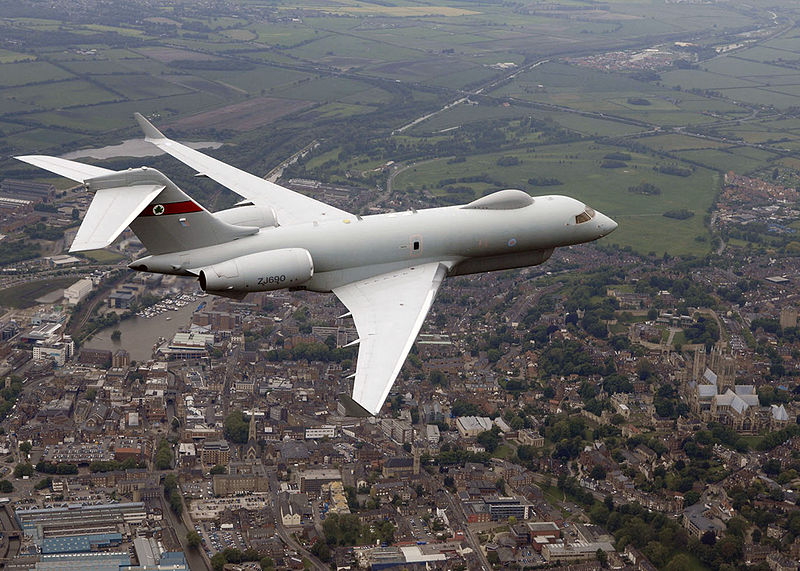
Sentinel_R1_MOD
Sentinel R1 – Source: Wikimedia Commons

Since the land grab by the self-proclaimed Islamic State (IS) in both Iraq and Syria, NATO’s EW assets have been targeting IS insurgents fighting units, gathering intelligence to offer tactical target info and to actively engage IS by denying rebel units radio communication and surveillance information – thus electronically blinding them. Sanitized intelligence information is shared with friendly forces including the rebel forces fighting against Syrian president Bashar al-Assad.

Until September 2015, Russia has been supporting Assad by supplying arms and training to Syrian forces. Bolstered by what it sees as Western indecisiveness on a Syria solution and by the West’s inaction on Russia’s military intervention in the Ukraine, Russia has decided to provide direct military air support to Syria. Nonetheless, Assad’s enemies comprise all rebel groups opposing his rule – not just IS.

The Cat & Mouse

So how can the Krasukha-4 be used to cloak Russia’s operations in Syria? In words – partially effectively. Its surveillance techniques won’t only be able to monitor NATO airplanes movement over Syria but also the types, and from its intelligence it’ll know the frequencies used and signal characteristics present – Lacrosse satellites and AWACS operate in S-band, Sentinel (and similar) in X-band, and drones in J-band. Lacrosse/Onyx satellite positions are regularly tracked by Russia. With this intelligence detail the Krasukha-4 could be programmed to engage so as to deny or disrupt NATO intelligence gathering.
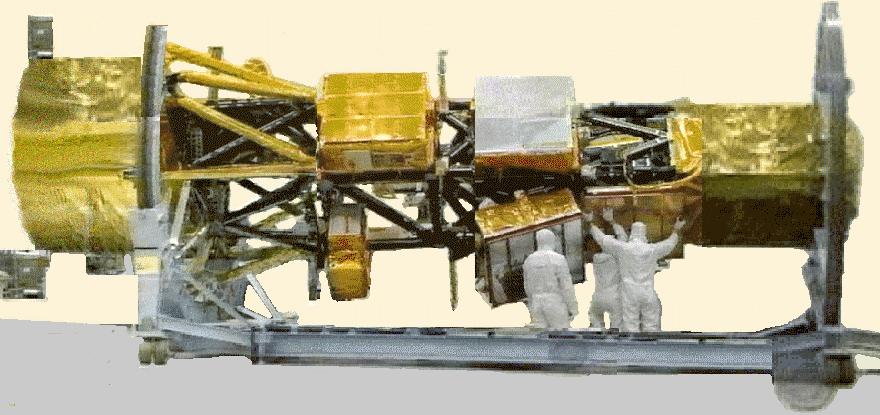
lacrosse
Lacrosse Satellite – A small surveillance satellite – Source: Globalsecurity.com

However it isn’t all one way – US and NATO intelligence gatherers will have “electronic counter counter measures” (ECCM) to fight Russian EW interference – and so the cat and mouse game of the Cold War is repeated. Intelligence gathering and radar-guided munitions will suffer some disruption and errors may be made however operations will continue.

ECCM might include being frequency agile and dodging the jamming signal or pointing the receiving antenna away slightly from the jamming source. There are additionally many methods that may be played with signal processing that can mitigate the effects of jamming. After all, it might even be possible for NATO to jam the Russian surveillance radar, denying them of identification and positioning of NATO planes – but this may really ramp up the confrontation with Vladimir Putin.

Russia will now be able to test its new EW techniques in live combat but avoiding direct conflict with NATO – it’ll improve overseas sales prospects of the Krasukha-4 system. NATO shall be in a position to test its ECCM against another EW system, presumably with similar ends in mind.

With a handful of fighter jets, just a few naval assets, a jammer, and a signals intelligence aircraft, Putin has managed to reshape the balance of power in Syria. It’s what Sutyagin, who spent 11 years in jail in Russia on flimsy espionage charges that brought on human rights groups to label him a political prisoner, called an enormous achievement “with tiny efforts.”

Tags: turkish log jammer, russian military, future power weapons
American Capital Harnessing Electrical Energy From Each Flush

2

The next time you flush in the capital of United States, you may think about this: You — or, more precisely, when ever anyone flushes — will assist in generating clean energy.

D.C. Water, which also treats sewage from much of the Maryland and Northern Virginia suburbs, recently became the first utility in North America to make use of a Norwegian thermal hydrolysis system to transform the sludge left over from treated sewage into electrical energy.

Yes, to put it bluntly, the city’s sewage treatment plant is turning poop into power.

“It is an enormous deal on so many fronts,” D.C. Water General Manager George S. Hawkins stated after Wednesday’s official unveiling of the system. “It’s a public utility leading the world in innovation and technology. We have private and public water firms coming from all around the world to see this.”

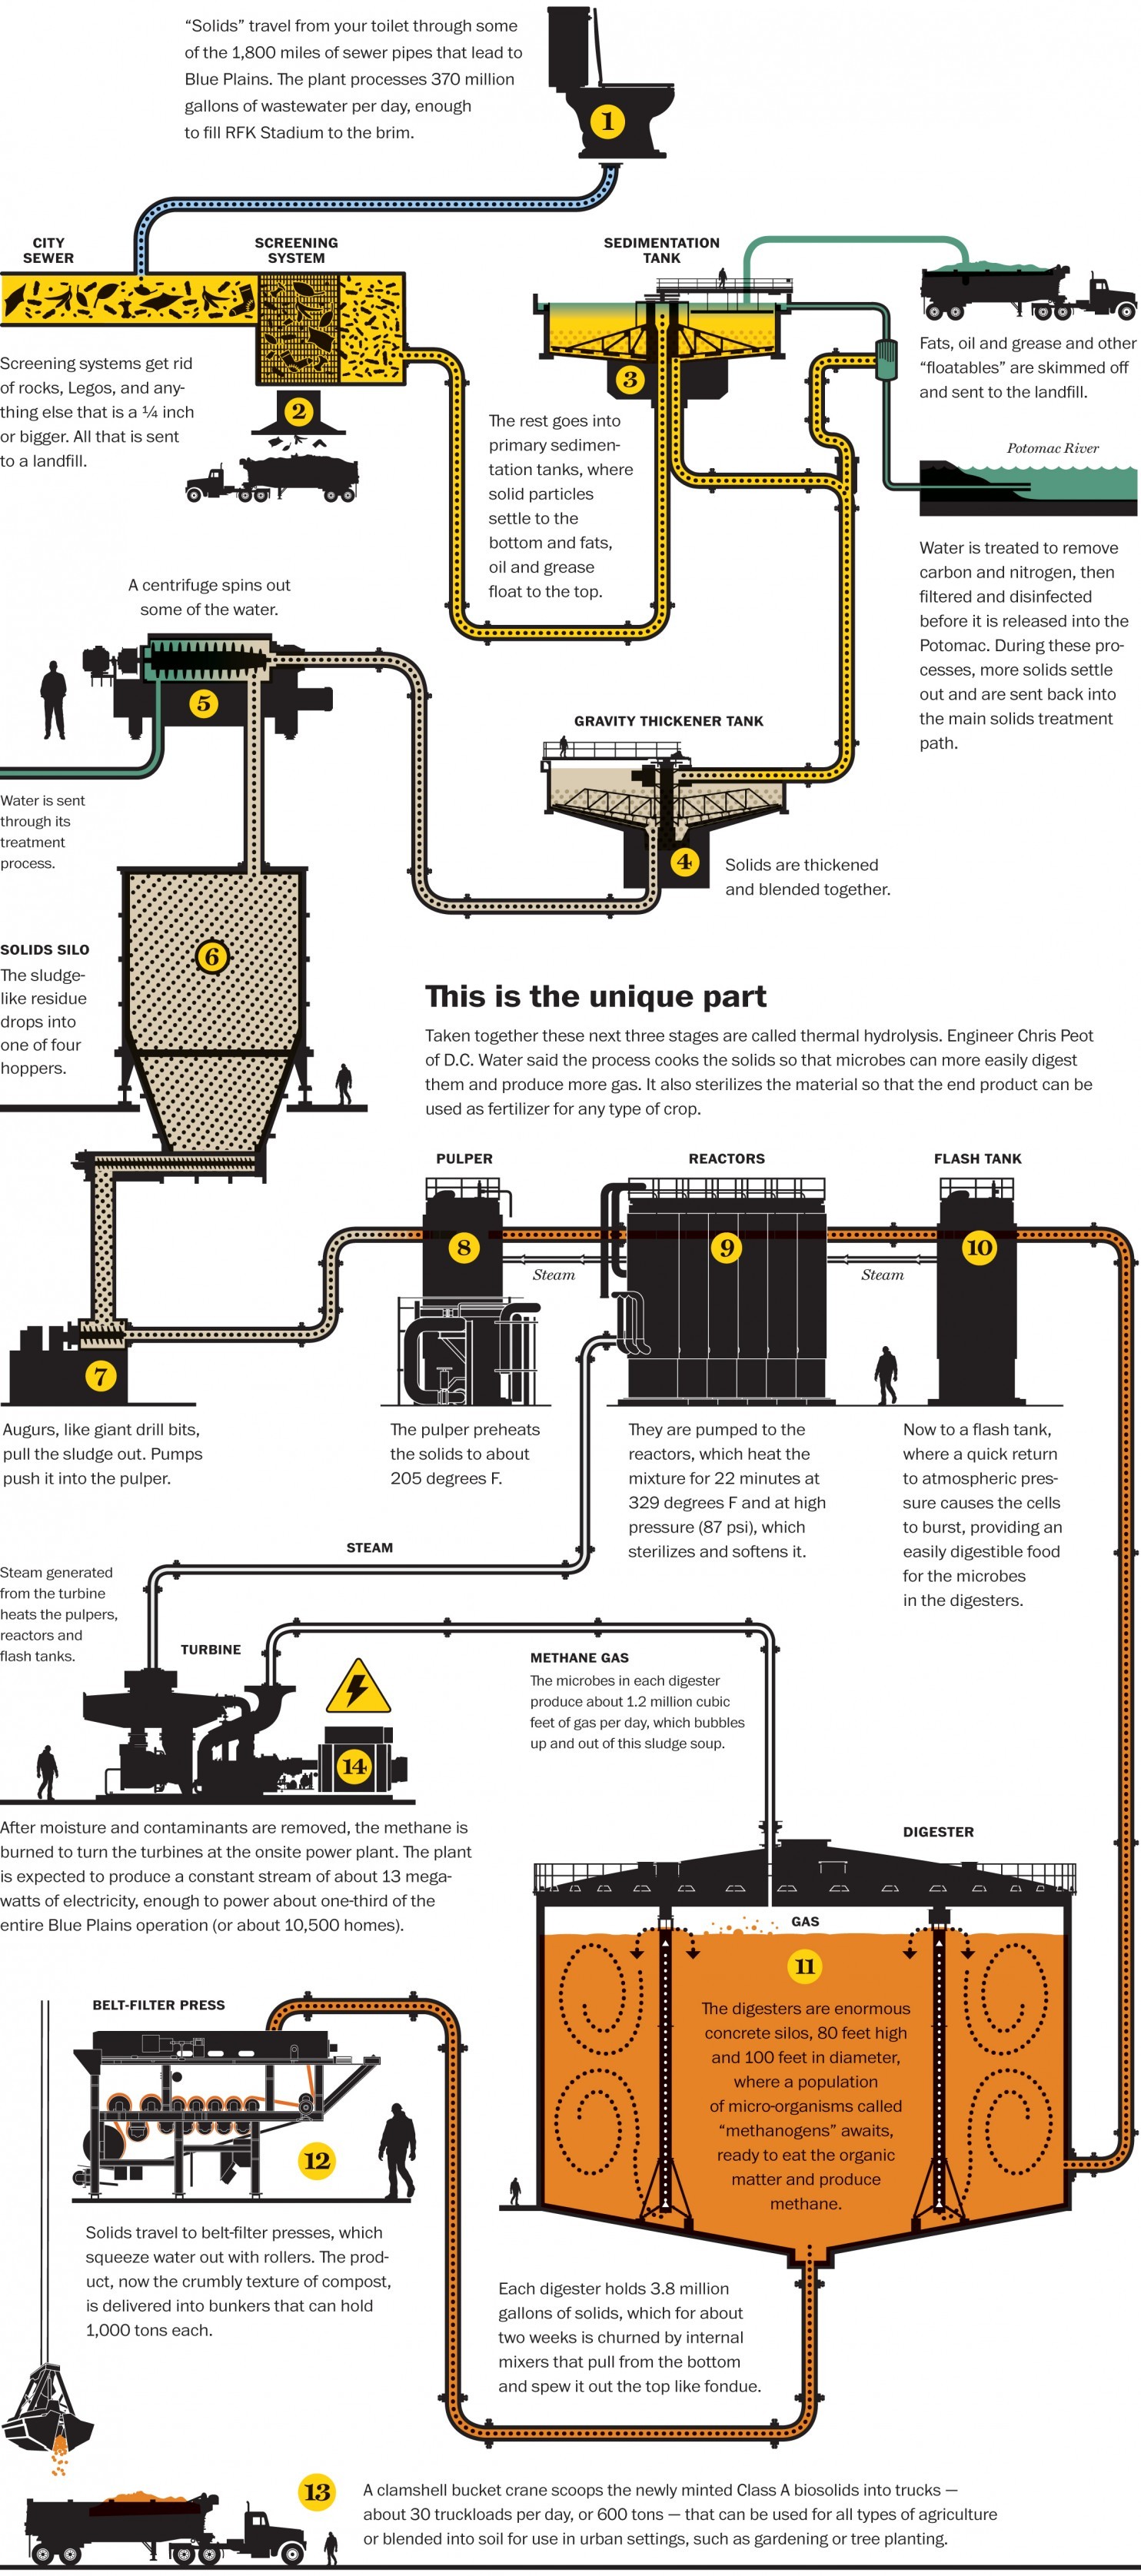
How Poop is turned into electricity - click for the complete image
How sewage is turned into electricity – click for the complete detailed image

However the Blue Plains Advanced Wastewater Treatment Plant, officials say, is the first in North America to do so using “pressure cooker” technology that can fit such a system in the relatively tight confines of an urban treatment plant. D.C. Water officials say it’s the biggest of its type on the planet.

Hawkins mentioned the system, which started producing electricity in September, will provide one-third of the 157-acre plant’s power, saving about $10 million yearly. Huge amounts of water and sewage need lots of energy to move via pipes and pumps, making D.C. Water the city’s largest consumer of electricity.

The utility expects to save an extra $2 million or so yearly on treatment chemicals and $11 million yearly in trucking expenses. Previously, the plant produced 1,200 tons of “Class B” biosolids every day, the industry term for the darkish gunk left over from treated sewage. That moist, smelly residue needed to be carried away in 60 truckloads every single day, traveling about seventy five miles to farms in Virginia. The new system produces about half as much of a cleaner “Class A” biosolid, which requires half the number of truck runs and smells less like poop and more like damp mulch.

The Class A compost-like substance may show up within the next year on the shelves of Home Depot as a soil nutrient for home gardens, officials said.

D.C. Water officials say the $470 million system, which took 4 years to construct, will end up paying for itself and shrink the plant’s overall carbon footprint by one-third.

At the dedication ceremony, officials from the U.S. Environmental Protection Agency and the U.S. Energy Department touted the system as an example of how localities can invest in infrastructure while conserving energy and cleaning the environment. Officials noted that water & sewer utilities account for 4% of the nation’s overall power usage, making them the biggest energy consumers in most communities.

D.C. Mayor Muriel E. Bowser (D) said the system dovetails with the city’s sustainability efforts.

“We can not afford to have waste be just waste,” Bowser stated. “Every dollar spent to transform that waste into energy will help us to reach our goals.”

Here’s the way it works: Once you flush or send soapsuds down the drain, the contents travel via miles of pipe and finally reach Blue Plains, off Interstate 295 in Southwest Washington . There, what appears like brown, murky water flows by screens that remove debris and then sits to allow solids to settle. Then, enormous centrifuges spin off the water and focus the remaining poopy solids.

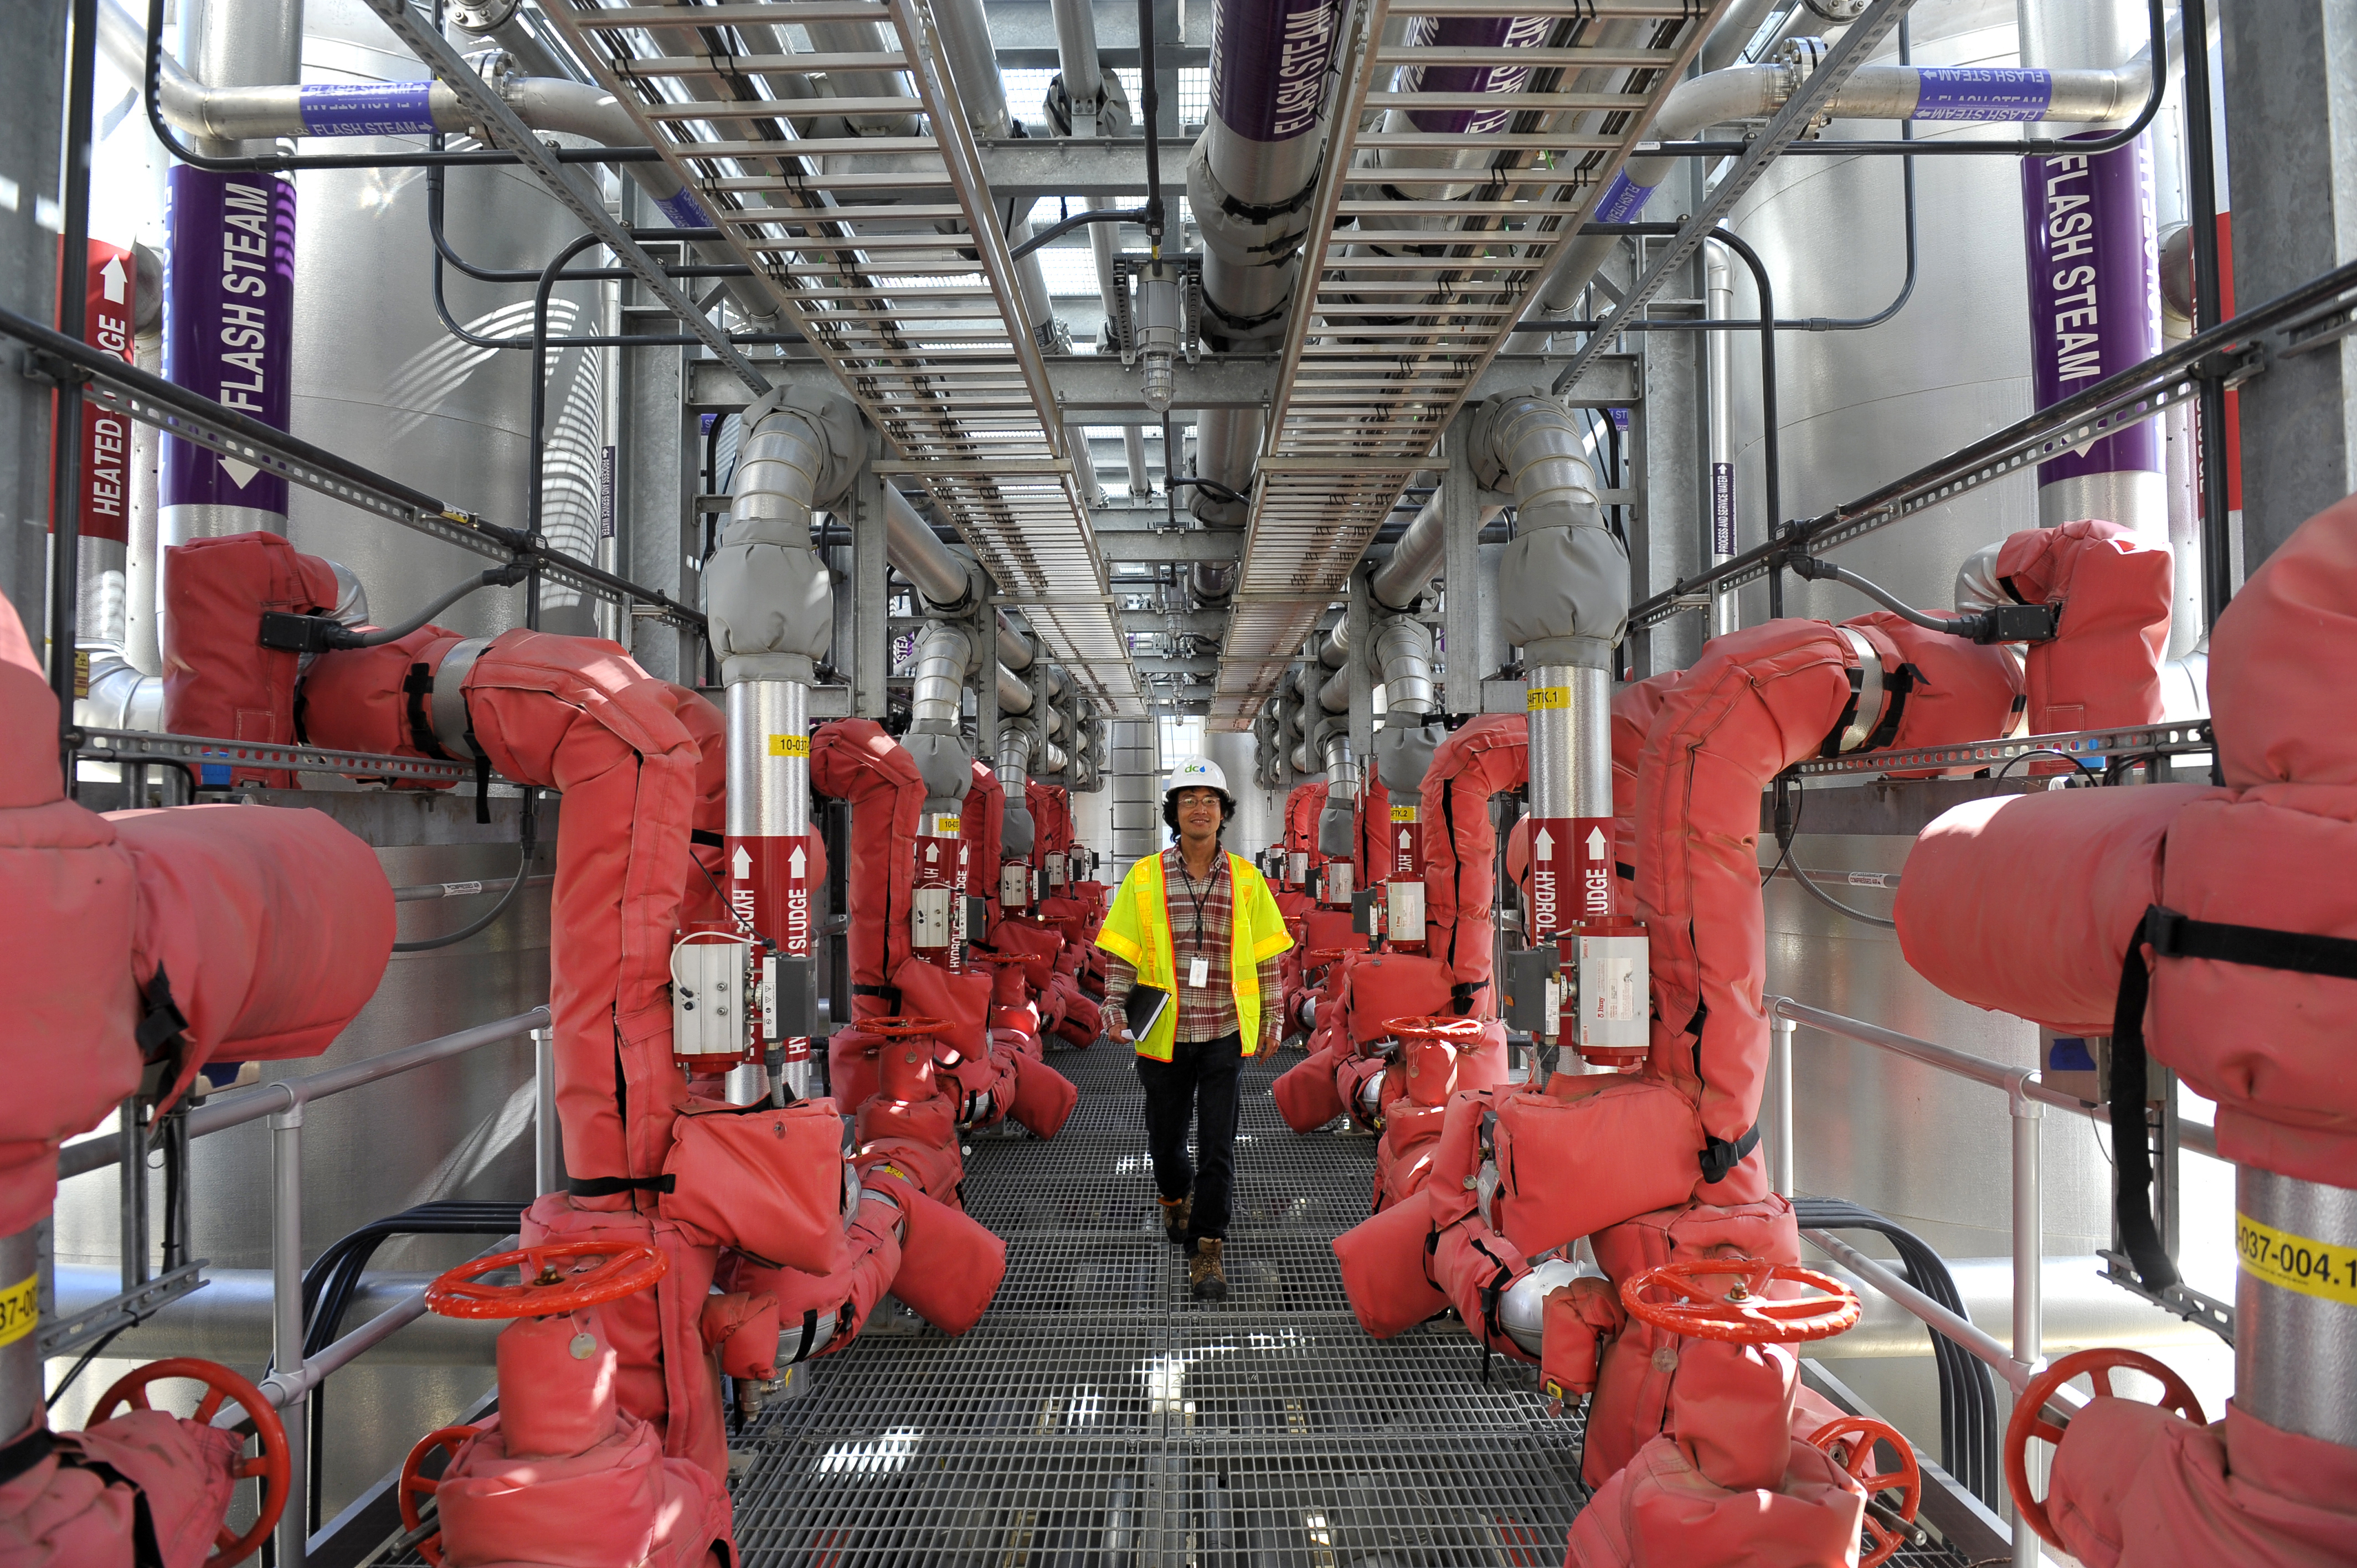
The liquid is sent off to be treated after which it returned to the Potomac River (yuck! and we thought only astronauts drank water purified from the piss), and the concentrated sludge is pumped into massive steel Cambi reactors, named for the Norwegian manufacturer. The reactors perform like pressure cookers, using 338-degree steam and pressure to cook the sludge. Then it gets pumped to another tank at a much lower pressure, which causes the cell walls of the unhealthful pathogens and other microbes to burst.

“We are not just burning up the bacteria,” Hawkins explained. “We completely destroy it.”

The sludge is then despatched into one of 4 “digesters” — concrete cylinder tanks as tall as eight-story buildings — that each hold 3.8 million gallons. There, it spends about three weeks as microbial bugs nibble at it. The bugs convert the organic matter into methane gas, which is cleaned and sent to a close-by building, where generators burn the methane gas and produce electricity. The entire system covers about 5 acres.

The key, Hawkins stated, is the Cambi pressure cookers that burn off a lot of the sludge, leaving less of it to be treated. That allowed D.C. Water to have only 4 monumental cylinder-like digester buildings instead of eight, which it didn’t have room for.

Hawkins lauded the group of local leaders for their support, saying that they and D.C. Water customers had made the venture possible.

A Router Virus That Actually Keeps You Safe!

Routers are amongst the most hackable devices connected to the internet — not often updated, easily compromised, and virtually never scanned for viruses. However a new router virus may actually be making the units safer, based on a report from the security firm Symantec. Dubbed Linux.Wifatch, the bug behaves like an everyday virus from the outside: infecting the system, operating undetected, and coordinating actions via a peer-to-peer network. However instead of performing DDoS assaults or on the lookout for sensitive information, Wifatch’s acts like a vigilante and its primary function appears to be protection from other malwares and viruses out there. It stays updated on virus definitions by way of its peer-to-peer network, deletes any spyware found, and cuts off different channels malware would usually use to attack the router. In short, Wifatch is actually defending its victims!

“To any NSA or FBI agents reading this: please consider whether defending the US constitution against all enemies, international or domestic, requires you to follow Snowden’s example.”

Most of Wifatch’s code is written in the Perl programming language and it targets several architectures and ships its own static Perl interpreter for each of them. Once a device is infected with the Wifatch, it connects to a peer-to-peer network that is used to distribute threat updates.

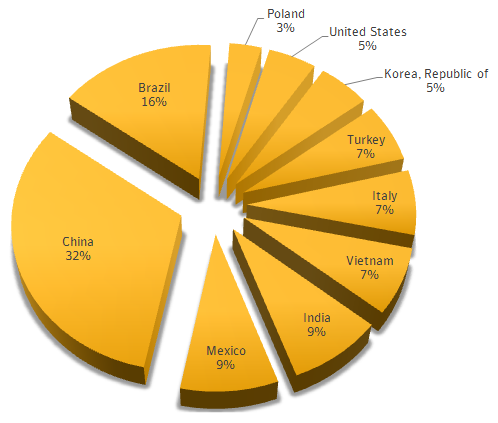
Breakdown of countries virus has infected
Breakdown of countries the virus has infected – Source: Symantec

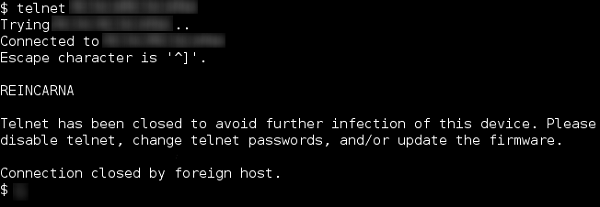
It is still unclear where Wifatch comes from or why it was created, nevertheless it appears to be completely different from the typical virus. First discovered in 2014, the virus appears to make little effort to hide itself, and leaves numerous benign messages in its code. One, triggered when a person tries to access the Telnet, reminds users to update the machine’s firmware. Another, dropped as a comment in the source code, repeats a statement from free-software activist Richard Stallman: “To any NSA or FBI agents reading this: please consider whether defending the US constitution against all enemies, international or domestic, requires you to follow Snowden’s example.”

wifatch message
Wifatch message when a user tries to access telnet

Symantec estimates “somewhere within the order of tens of thousands of devices” are contaminated with the virus, with infections largely centered in Brazil, China, and Mexico. Resetting the router is enough to remove the virus, however the firm warns that a router might become reinfected over time. “Symantec will be keeping a close eye on Linux.Wifatch and the actions of its mysterious creator,” the post concludes. “Customers are suggested to keep their system’s software and firmware updated.”

Weekly Science News: 25th September – 2nd October, 2015

1

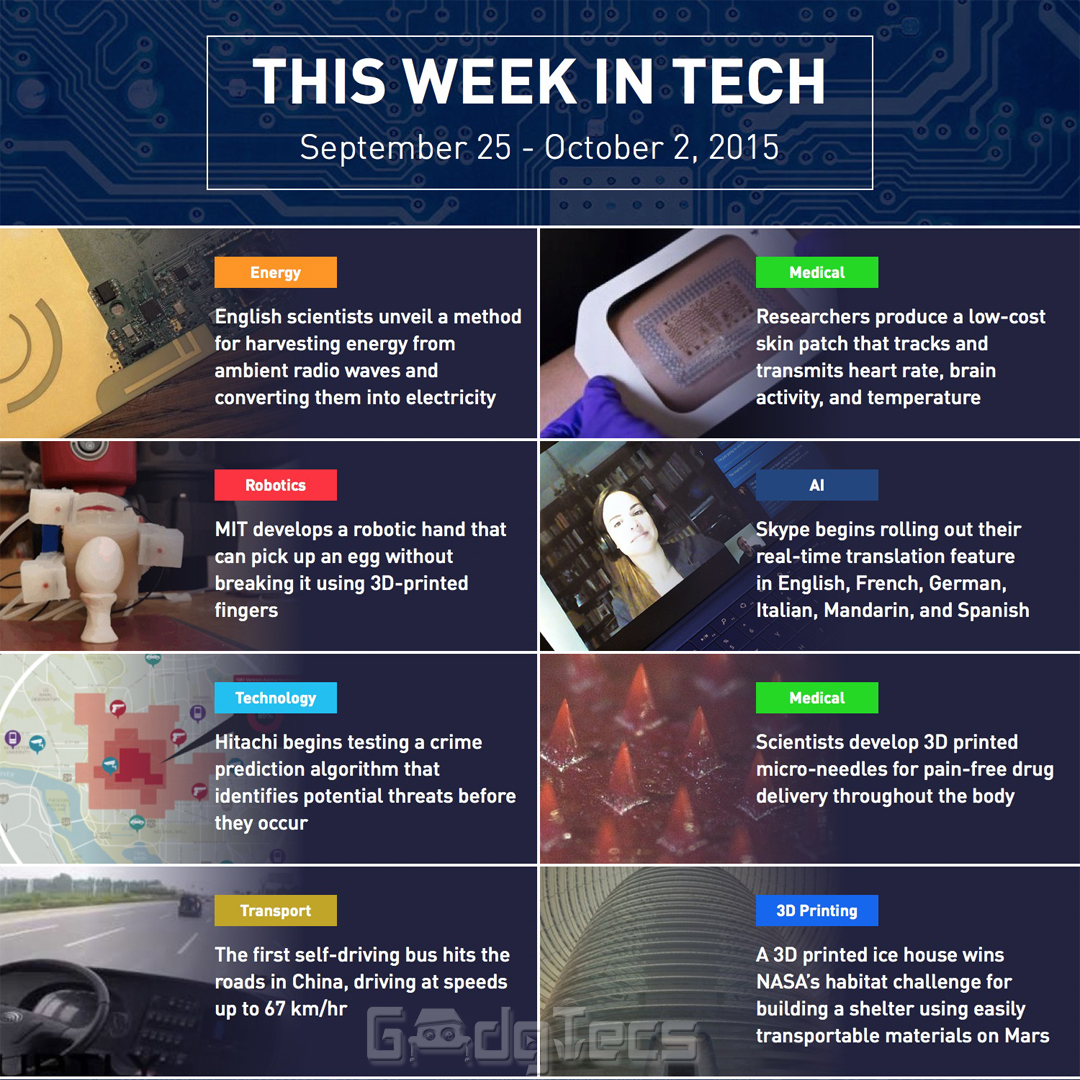
News: Brief Updates from the world of science for the week from 25th September 2015 to 2nd October 2015.

This week in #Science – 25th September to 2nd October

A photo posted by GadgTecs (@gadgtec) on

Reviews: The E-Blade Self Balance Board

8

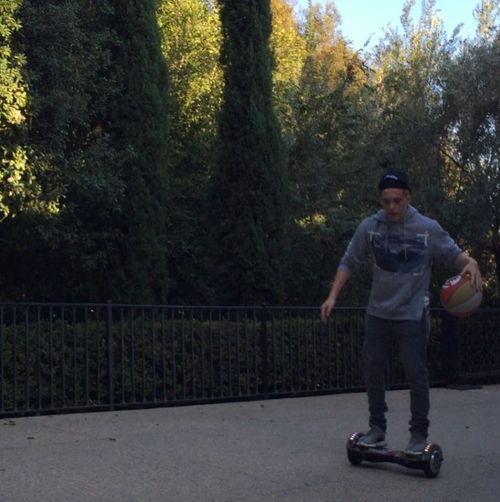
In recent months, the popularity of the self-balance scooter (or the Segway hoverboard as the cool kids call them) has exploded with an array of celebs including the Biebs, Brooklyn Beckham, and even a Kardashian ditching their boots and heels for motors and wheels.

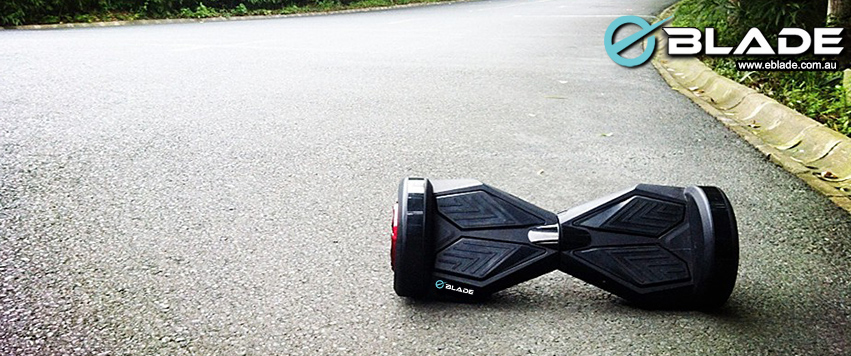
brooklyn-beckham-segway-board The eblade self-balance board is powered by two gyroscopic motors that use similar technology found in the original Segway but in a much more compact package. The inbuilt gyros maintain a level platform for the rider who controls the scooter by leaning on the smart pedal pads under each foot. The pedals are highly sensitive and require only the slightest of movements to propel the rider in any direction.

#tricks like #skateboarding plus it pushes uphill for you! #paddlingout

A post shared by eblade (@eblade_official) on

The scooters have attracted the “hoverboard” title from the public as they make the rider look like they’re floating. The effortless appearance of using the scooter only takes a few minutes to achieve as the rider becomes accustomed to the controls. Most users pick it up in around ten minutes and have it clocked in half an hour. The main thing to remember when riding is to let the scooter do all the work and try and keep your body in an upright position. Once you’ve got that thought cemented in your brain, it doesn’t take long before you’re zooming around the neighbourhood.

Eblade Smart Balance Board Specs

  • Charge time: 2-3 hours
  • Distance per charge: 25km (15.5 miles)
  • Max speed: 12km/h (7.5 mph)
  • Weight: 11kg (24 pounds)
  • Built-in Bluetooth speakers
  • Samsung lithium ion battery
  • Price: $799 AUD (561 US$ at the time* of posting)
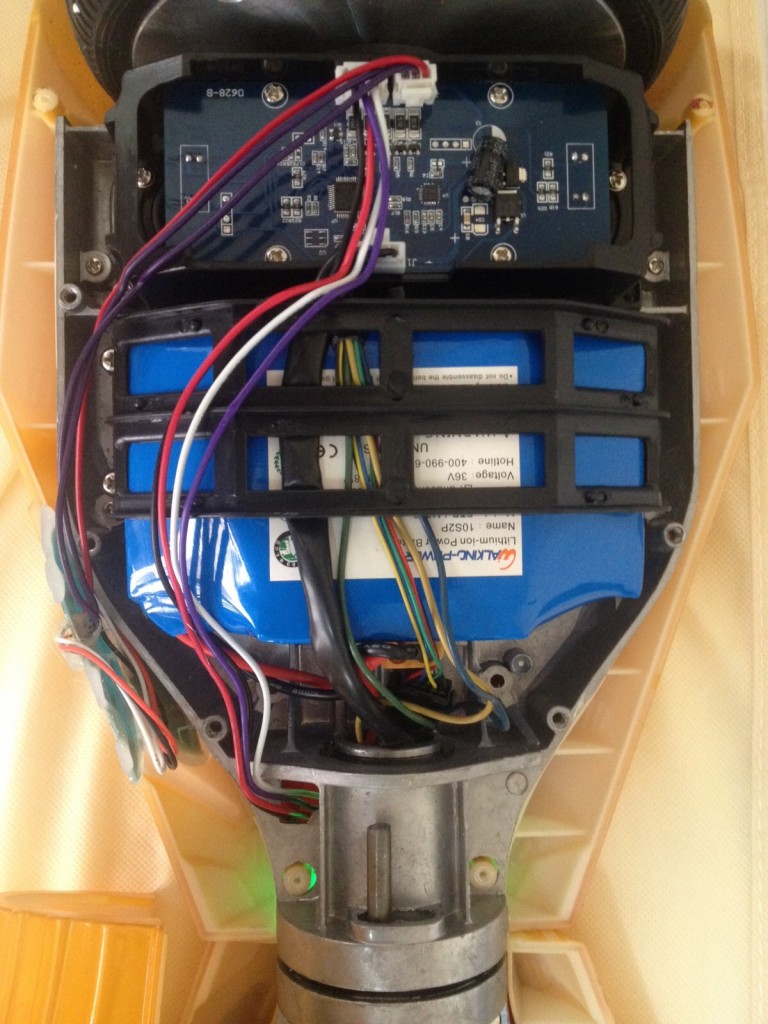
inside of an e-blade
Inside of an E-blade: very well built with a large battery

How practical the eblade scooter will be as an alternative mode of transport remains to be seen as it may take a while before the public adopt the scooter as a legitimate form of transport. But if you take into account the growing cost of owning a car in many countries, as well as the rising costs of public transport; the eblade scooter does become a more viable and eco-friendly option. The rechargeable Samsung lithium ion batteries are capable of supporting a 25km range which means workers who live close to the city can easily commute to work and back on a single charge, reducing the amount of cars on the road and also saving on parking!

Apart from the practical side of the scooter, these things are unbelievably fun to ride, turning every road and footpath into an adventure as you cruise through the once mundane city streets. The scooter also comes with built-in Bluetooth speakers so you can pump out your favourite tunes as you cruise.

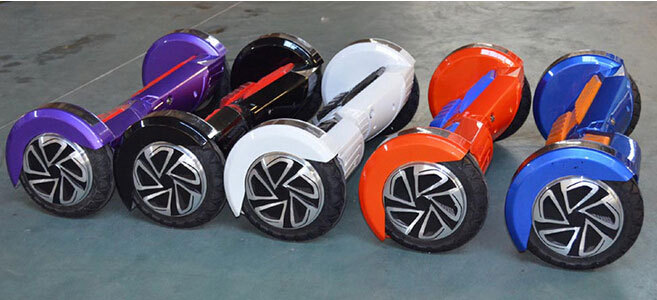
mini segway range

The eblade balance board is an absolute blast, and more practical than you think! So if you’ve got some spare cash and want a new way to get around the city why not add this to your Christmas list!

*30th September 2015

Scientists have found a new way to edit DNA

3

A FEW years in the past, molecular biologists made an enormous breakthrough. By borrowing an antiviral mechanism from bacteria, they created a simple method to tweak the genetic data inside cells – a method that had huge implications for science, medicine & agriculture. However, a dispute over who precisely invented what first has threatened to curtail its potential. But CRISPR-Cas9, as the disputed technique is known as, turns out to not be the only means bacteria defend themselves from the attentions of viruses.Recently, in Cell, a group of researchers led by Feng Zhang of the Broad Institute in Cambridge, Massachusetts, who is among the parties to the patent dispute, have announced their discovery of another such mechanism.

Like its predecessor, the new mechanism, called CRISPR-Cpf1, has the potential to turn into a tool that may deal with intractable genetic diseases such as Huntington’s, and degenerative conditions like Alzheimer’s. It may also be used to create new classes of anti-viral treatment, and thus curb infectious disease. Plant and animal breeders, as well as doctors, might find it helpful, too. They could create new strains of crops and livestock. Indeed, because, like CRISPR-Cas9, it doesn’t involve taking genes from one organism and implanting them in another, it is not going to count as “transgenic”, a bogeyman of campaigners and customers alike.

CRISPR-Cas9 consists of a molecular pair of scissors (the Cas9) and a guide sequence of DNA (the CRISPR) that tells the scissors where to chop. The dispute over who can rightfully claim inventorship has prompted some, although not all, potential companies to give the technology a wide berth. Monsanto, a plant-breeding and agrichemicals agency, has gone on record as saying that it’s reluctant to make use of CRISPR-Cas9 widely till it understands the intellectual property concerned. Drug corporations have also circled at a distance. CRISPR-Cpf1, which has a different pair of scissors, might effectively not endure these legal issues.

CRISPR-Cpf1 can also be better than CRISPR-Cas9 in other ways. Cpf1 is a smaller and less complicated enzyme (identified technically as an endonuclease) than Cas9, which suggests it is going to be simpler to deliver to the cells whose genes need modifying. And its slightly offset cuts to double-stranded DNA will help researchers to insert genetic patches more effectively and precisely.

Its discovery also raises the question of how many other endonuclease-based systems are out there in the world’s bacteria. Viral infection is a serious threat to these microbes, and the natural job of both CRISPR-Cas9 and CRISPR-Cpf1 is to recognise viral genes and chop them up before they can do any harm. Conversely, viruses are constantly evolving to escape the antiviral systems’ attentions, meaning bacteria need to generate new ones. The chances are good, therefore, that CRISPR-Cas9 and CRISPR-Cpf1 are not alone. As Dr Zhang himself puts it, “I can’t even begin to count how many there may be. There really is great diversity that we as a scientific community should go out and explore.”

edit genes
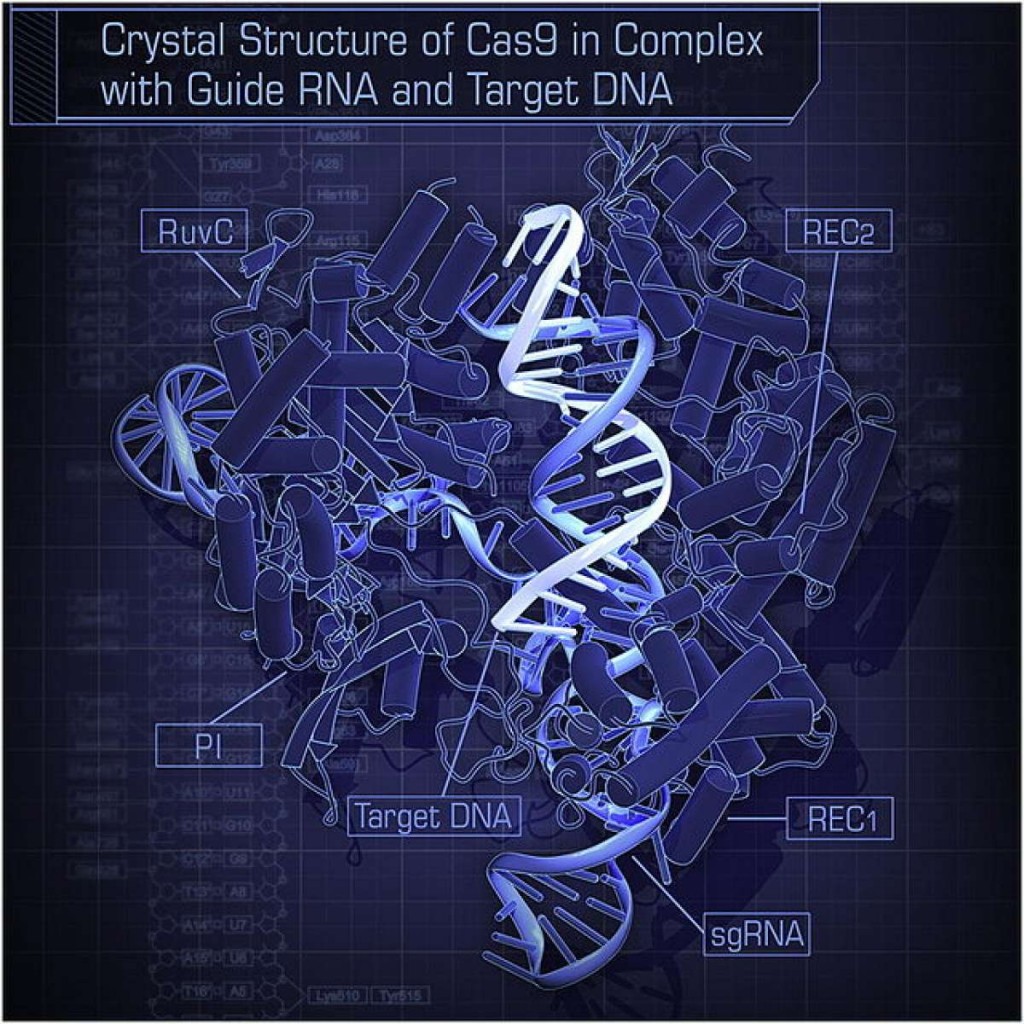
Crystal Structure of cas9 in_complex with guide rna and target dna

The tools to carry out that exploration now exist. CRISPR-Cpf1, for instance, was found not by searching in bacteria directly, but by scrutinising a published database of bacterial genetic sequences, which yielded two species that contain it. Further searches might be equally rewarding—and the more gene-editing systems are discovered, the harder it will be to monopolise their use.

Despite the optimism of those who think the new techniques may calm qualms about genetic engineering, however, some people are bound to have ethical worries—certainly when it comes to applying them to human beings. Earlier this year, for example, when Chinese scientists used CRISPR-Cas9 gene editing on a human embryo (albeit one that was unviable, and could not therefore have developed into a person) there was much brouhaha and several calls for a moratorium on this line of inquiry.

In December, therefore, a group of academic societies from America, Britain and China are hosting a meeting in Washington, DC, to thrash out some of the issues—particularly about the way in which gene editing might be used to make changes in human beings that could be inherited. On September 18th researchers in Britain applied for permission to modify human embryos genetically, as part of a study of human development. Any licence would allow the use only of embryos left over after IVF treatment, and those embryos could be studied for no more than two weeks of development. Nor could they be used to create a pregnancy, or for any other clinical application. But the direction of travel is clear.

The Washington meeting is thus timely. Scientists need to set out to politicians, and to the public at large, what gene-editing technology can now do. They could also speculate usefully about what it might mean for the future, and how best to use it. Dr Zhang is one of those who will attend. He will say that it is the responsibility of scientists and developers of the techniques to make sure that they engage the public in thoughtful discussion, and that the technology is used to best advantage.

This is a responsible attitude, and reminiscent of a meeting that happened 40 years ago in Asilomar, California, when early genetic engineers got together to explore the implications of their science. Then, they agreed a strict set of safety conditions and a self-imposed moratorium on some sorts of research that might have been dangerous, which helped to allay public fears. As more recent experience with genetically modified crops has shown, it is important to be up-front and open in this way. It would be a pity if CRISPR-based gene editing, having escaped the legal thickets, were to get tangled up in a PR disaster.

Engineers invent clear coating that boost solar cell efficiency by cooling them

2

The hotter solar cells turn out to be, the less efficient they’re at converting sunlight to electrical energy, an issue that has long vexed the solar trade. Now, Stanford engineers have developed a clear transparent overlay that will increase efficiency by cooling the cells even in full direct sunlight.

When laid over a photo voltaic cell, the clear materials shown here can radiate heat away from photo voltaic cells, allowing them to produce electricity extra efficiently.

Every time you stroll outside you emit energy into the universe: Heat from the top of your head radiates into space as infrared light.

Now three Stanford engineers have developed a technology that improves on solar panel efficiency by exploiting this basic phenomenon. Their invention shunts away the heat generated by a photo voltaic cell under sunlight and cools it in a manner that enables it to convert more photons into electrical energy.

The work by Shanhui Fan, a professor of electrical engineering at Stanford, research associate Aaswath P. Raman and doctoral candidate Linxiao Zhu is described in the current issue of Proceedings of the National Academy of Sciences.

The group’s discovery, tested on a Stanford rooftop, addresses a problem that has long bedeviled the solar industry: The warmer photo voltaic cells get, the less efficient they become at converting the photons in light into useful electrical energy.

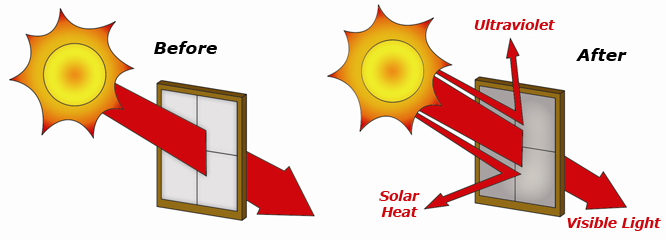
The Stanford solution relies on a thin, patterned silica material laid on top of a conventional solar cell. The material is transparent to the visible light that powers solar cells, but captures and emits thermal radiation, or heat, as infrared rays.

“Photo voltaic arrays should face the sun to perform, despite the fact that that heat is detrimental to efficiency,” Fan stated. “Our thermal overlay permits sunlight to pass through, preserving or even enhancing sunlight absorption, but it also cools the cell by radiating the heat out and improving the cell efficiency.”

A cool method to enhance solar efficiency

In 2014, the same trio of inventors developed an ultrathin material that radiated infrared heat directly back towards space with out warming the atmosphere. They presented that work in Nature, describing it as “radiative cooling” because it shunted thermal power straight into the deep, chilly void of space.

In their new paper, the researchers applied that work to improve solar array efficiency when the sun is thrashing down.

The Stanford group tested their technology on a customized solar absorber – a device that mimics the properties of a solar cell with out producing electricity – coated with a micron-scale pattern designed to maximise the capability to dump heat, in the form of infrared light, into space. Their experiments confirmed that the overlay allowed visible light to go through to the photo voltaic cells, however that it also cooled the underlying absorber by as much as 23 degrees Fahrenheit.

For a typical crystalline silicon solar cell with an efficiency of 20%, 23 F of cooling would enhance absolute cell efficiency by over 1%, a figure that represents a significant gain in power production.

The researchers said the brand new clear thermal overlays work best in dry, clear environments, that are also preferred sites for large photo voltaic arrays. They believe they’ll scale things up so commercial and industrial applications are possible, perhaps utilizing nanoprint lithography, which is a typical approach for producing nanometer-scale patterns.

“That is not necessarily the only method,” mentioned Raman, a co-first-author of the paper. “New techniques and machines for manufacturing these sorts of patterns will continue to advance. I am optimistic.”

Cooler vehicles

Zhu stated the technology has a lot of potential for any outdoor device or system that demands cooling but requires the preservation of the visible spectrum of sunlight for either practical or aesthetic reasons.

heat reflection
It works in a similar way to heat reflective glass or paint, like the one illustrated above

“Say you’ve got a car that’s bright red,” stated Zhu, co-first-author of the paper. “You actually like that colour, however you’d also wish to benefit from anything that might assist in cooling your car during scorching days. Thermal overlays will help with passive cooling, however it’s an issue if they are not absolutely transparent.”

That is because the perception of colour requires objects to reflect visible light, so any overlay would must be clear, or else tuned such that it will absorb only light outside the visible spectrum.

“Our photonic crystal thermal overlay optimizes use of the thermal portions of the electromagnetic spectrum with out affecting visible light,” Zhu said, “so you’ll be able to radiate heat effectively with out affecting colour.”


Deep Sweep Launched by Hackers to Spy on Drones

For governments trying to hide controversial programs from their residents, there are few better directions to transmit secret military & spy communications than straight up. Unlike here on earth, no pesky amateur radio eavesdroppers or curious hackers monitor the open sky between ground control and a drone—not to point out between that drone and its communication satellite perched even more kilometers higher up.

Deep Sweep helium
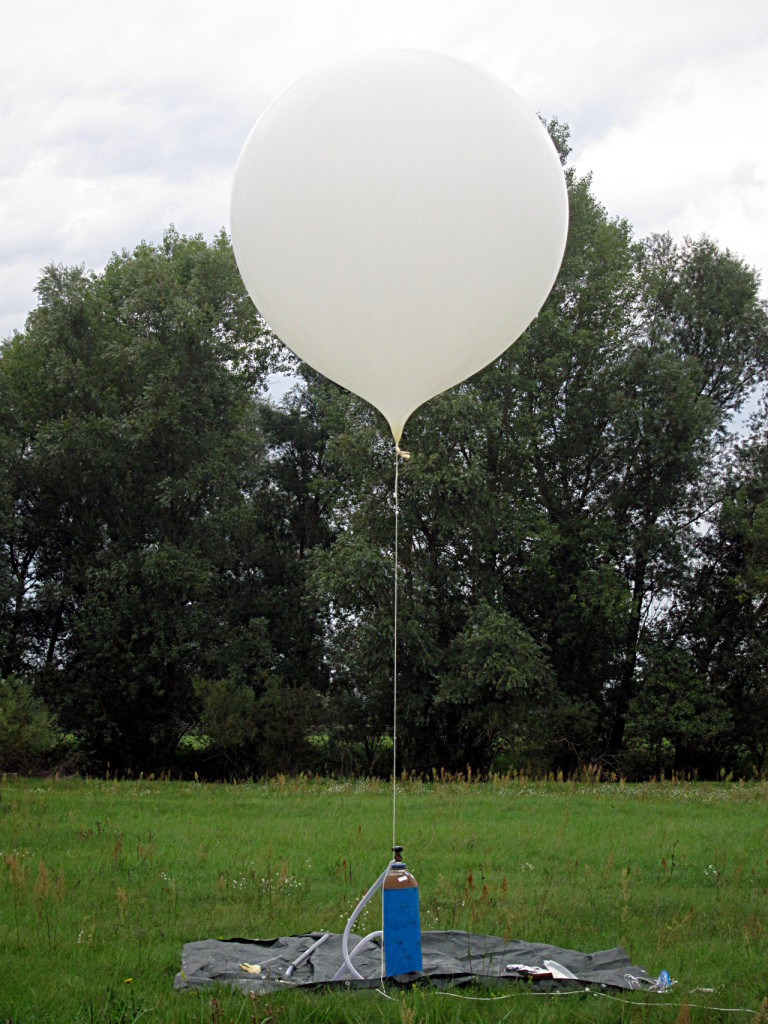
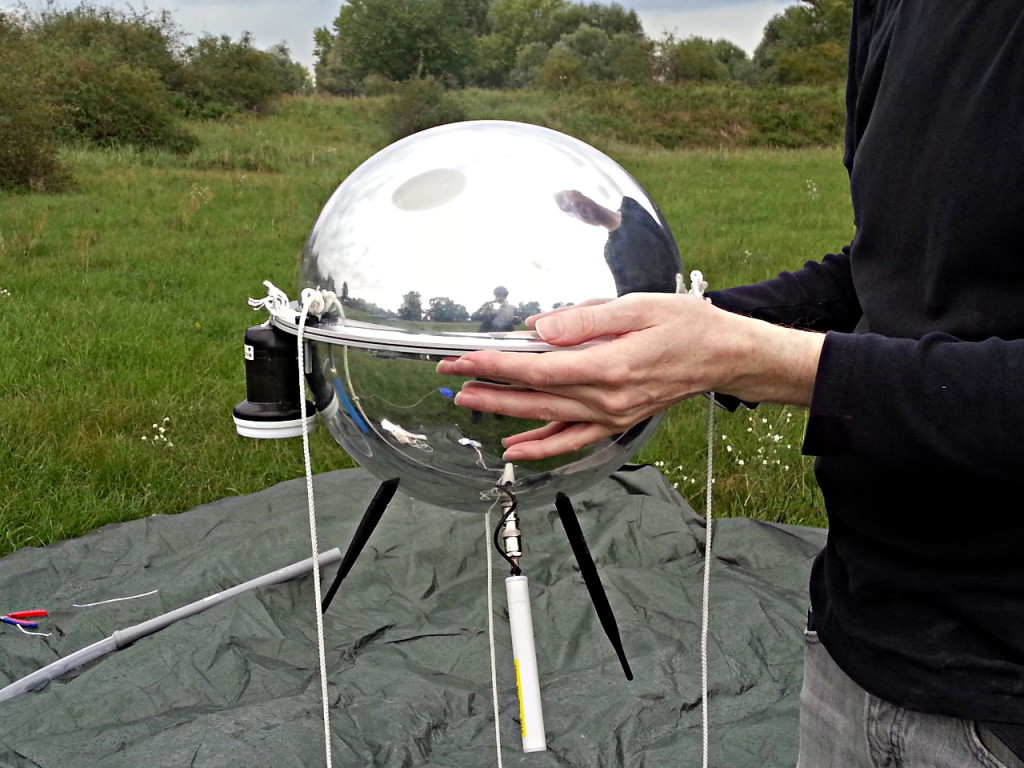
The weather balloon before launch. JULIAN OLIVER, BENGT SJÖLEN & DANJA VASILIEV

One small crew of hackers is attempting to pierce that stratospheric secrecy zone with a high-altitude flying, or floating, machine of their own. The three members of a socially motivated movement of technologists referred to as Critical Engineering have developed and begun testing an “aerospace probe” they named the Deep Sweep. The invention, described in their own detailed write-up, is a 1-foot-diameter acrylic orb full of radio tools and connected to a 2.5-foot diameter helium-filled weather balloon. As it floats up more than 24 kilometers (15 miles) into the earth’s atmosphere, the probe’s antennae are designed to record a wide range of radio data to be analyzed when the probe is recovered hours or days later. The undertaking’s objective: to pioneer a brand new type of public, crowd-sourced data collection for monitoring the communications of a secret layer of government sky machines—UAVs aka drones, satellites and high-altitude planes.

“The core aim of the project is to build a low-cost platform for high-altitude signals intelligence for the rest of us,” says Julian Oliver, a Berlin-based artist and hacker who launched the venture together with fellow creators Bengt Sjöle & Danja Vasiliev. “It’s about creating an interface to read the signals in the skies above us, to understand what’s happening up there.”

Inside Deep Sweep
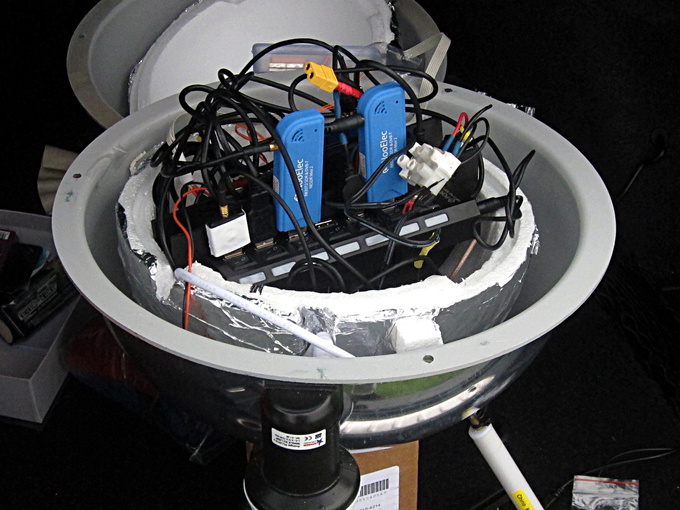
Probe with hardware inside styro-foam insulation shell, mounted inside acrylic exo-shell. JULIAN OLIVER, BENGT SJÖLEN & DANJA VASILIEV

The group’s DIY probe was constructed with three software defined radios, three antennae all listening to different parts of the radio frequency spectrum, a GoPro camera, a GPS module, temperature and pressure sensors, a SIM card for communicating with the crew through SMS, and an insulated battery. All of that’s integrated with an Arduino board, a USB hub, an Intel Edison minicomputer and open-source software program. The cheap design is meant to encourage other amateurs to construct high-flying probes of their own: Oliver says the complete setup cost less than $300—although they hope to use even cheaper parts in future versions—with another $200 for the balloon plus the helium to fill it.

As a final touch, the group constructed the orb’s shell from a pair of parabolic mirrored surveillance camera covers—the sort used on the ceilings of retail stores and banks. “We thought that suited the project very nicely,” Oliver says.

To this point, the Critical Engineers have staged two test-launches of their spy balloon. Here’s the way it works: When the probe rises to an altitude of around 30 kilometers (18.6 miles), low atmospheric air pressure causes the balloon carrying it to burst (after expanding to almost 10 times its original size). Then the probe releases a nylon parachute and floats safely back to earth. Once it’s back in cell tower range, it sends a text message to its creators signaling its arrival and sharing its landing location.

The tests had mixed outcomes. Its first balloon flight from the eastern German city Frankfurt in August landed in a Polish field. When they tracked down and recovered the machine after a long, pre-dawn drive, they discovered that its energy source had failed just seven minutes into the flight, cutting short its data collection.

Their second launch later in the same month was more fruitful, despite a different set of issues: They released the balloon from Magdeburg, Germany, anticipating that it will again land in Poland. Instead, during a long interval when the probe lost cell signal, the wind pulled it more more than a 1000 kilometers (~600 miles) east, at some points dragging it through the sky as fast as 140 km/h (87 m/hr). “It was a bit of a desperate feeling,” says Oliver. “You get quite hooked up to the thing. After we finally received an SMS from it the next morning, we were very happy.”

Deep Sweep
View from the probe as it climbs into the stratosphere, overlaid with the radio frequency and power data it collects. JULIAN OLIVER, BENGT SJÖLEN & DANJA VASILIEV

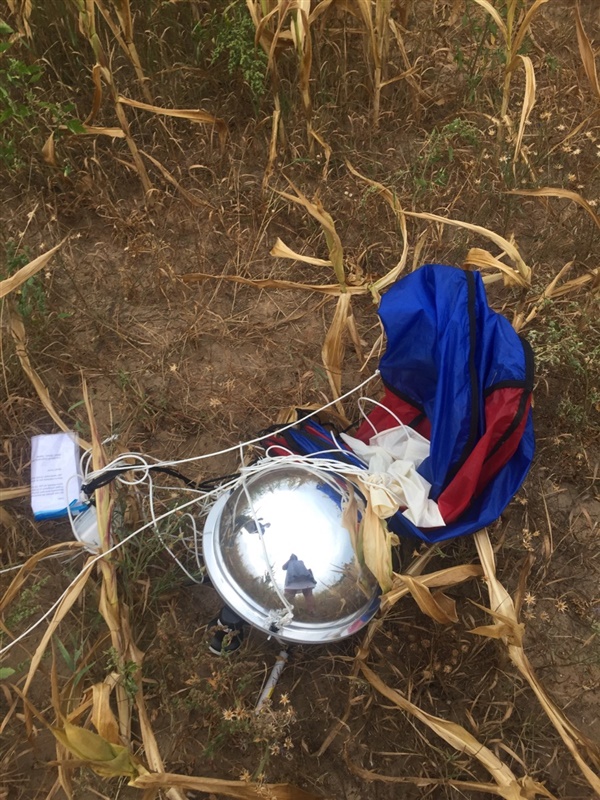
The probe had landed in a cornfield close to Minsk, Belarus. Since Belarus’s dictatorship doesn’t maintain an open border with the EU, the crew needed to enlist the assistance of a buddy with Belarusian contacts to rescue it. Despite their initial suspicions that the shiny sphere’s creators were state spies rather than amateur hackers, a Belarusian couple finally retrieved the probe and offloaded its data over the Internet to Critical Engineering’s server in Sweden. (One of the two Belarusians traveled this month to Stockholm via a ferry from Estonia to deliver the probe back to its owners).

The info from that first successful test-flight, accessible here and constructed into a set of data visualizations here, is meant to be the start of a public, crowd-sourced collection. Oliver says the group plans to create a wiki for publishing the results of any future probe launches, both those by his Critical Engineering team and anybody else who launches a stratospheric radio balloon of their own.

Deep Sweep on Touchdown
Deep Sweep after its touchdown in a Belarusian cornfield. JULIAN OLIVER, BENGT SJÖLEN & DANJA VASILIEV

And just what do Deep Sweep’s creators think they’ll discover in their probe project’s potential trove of radio information? Oliver says they hope to pick up threads of conversation between government agencies and flying machines that range from Predator and Reaper drones to spy satellites like those launched by the U.S.’s secretive National Reconnaissance Office. Those radio conversations are no doubt encrypted, and Oliver says the group has no illusions that they’ll be capable of peering into the content of the communications. However they do hope they’ll ultimately have the ability to at least recognize the presence of secret sky gadgets talking to satellites overhead or the ground below, and even possibly learn to “fingerprint” and distinguish them.

Oliver hopes that the Deep Sweep project might be the start of a new amateur community of high-altitude radio fanatics who monitor the radio frequencies of the sky the same way that Ham radio hobbyists have monitored and transmitted ground-based communications for  years.

“What the Ham radio scene does here on earth…we wish to do the same thing at the fringe of space. Because that’s where a hell of a lot of really fascinating and dubious things are taking place,” says Oliver. “There’s no other way of getting to the bottom of it all than by getting up there.”

Launch Video


AI – Computer Learns From Mistakes – Becomes ‘Chess GrandMaster’

1

A computer program called Giraffe has taught itself to become an international grand master after playing itself for just 72 hours. The software was able to learn from its own mistakes as it played against itself and is now able to beat most humans who have spent a lifetime learning the game.

The software can play with itself and perfect the moves by detecting previous mistakes. It can also find alternative combinations for every set.

To be crowned as “Grandmaster” in chess, a player must be able to have a rating of more than 2,500. The world’s current number one player, Magnus Carlsen, was rated at 2,853.

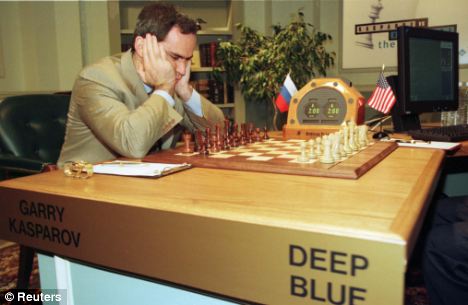
It’s been nearly 20 years since IBM’s Deep Blue supercomputer beat the reigning world chess champion, Gary Kasparov, for the first time under standard event rules.  Since then, chess-playing computer systems have developed considerably powerful, leaving the best humans little likelihood even against a modern chess engine running on a smartphone.

Gary vs IBM
Gary Kasprov playing against Deep Blue – 1997 – Source: Reuters

However while computers have become faster, the way chess engines work has not changed. Their power depends on brute force, the process of looking through all possible future moves to seek out the most effective next one.

Of course, no human can match that or come anyplace close. While IBM’s Deep Blue was searching some 200 million positions per second, Kasparov was probably searching not more than 5 a second. And yet he performed at essentially the same level. Clearly, humans have a trick up their sleeve that computers don’t (yet).

This trick is in evaluating chess positions and narrowing down the most profitable avenues of search. That dramatically simplifies the computational process because it prunes the tree of all doable moves to only a few branches.

Computers have never been good at this, but that changes thanks to the work of Matthew Lai at Imperial College London. Lai has created an artificial intelligence machine, which he calls Giraffe that has taught itself to play chess by evaluating positions much more like humans and in a completely different technique to conventional chess engines.

Lai generated his dataset by randomly choosing 5 million positions from a database of computer chess games. He then created greater variety by adding a random legal move to each position before utilizing it for training. In total he generated a hundred and seventy five million positions in this method.

The usual way of training these machines is to manually evaluate every position and use this information to teach the machine to recognize those that are robust and those that are weak.

However this can be an enormous task for 175 million positions. It might be carried out by another chess engine but Lai’s objective was more ambitious. He wanted the machine to be taught itself.

As an alternative, he used a bootstrapping approach in which Giraffe played against itself with the aim of enhancing its prediction of its own evaluation of a future position. That works because there are fixed reference points that ultimately determine the value of a position—whether or not the match is later won, lost or drawn.

Lai says this probabilistic approach predicts the best move 46 percent of the time and places the best move in its top 3 ranking, 70 percent of the time. So the computer doesn’t have to bother with the other moves.

Robot playing chess
Source: https://www.lkessler.com/brutefor.shtml

In a report from Daily Mail, Mr. Lai admitted that his software was not as good as the best chess software.  “Giraffe is able to play at the level of an FIDE International Master on a modern mainstream PC,” says Lai. By comparison, the top engines play at super-Grandmaster level.

Source – Giraffe: Using Deep Reinforcement Learning to Play Chess 


A Malware Called Active VisitorTracker Campaign Infecting WordPress Sites

3

For the last couple of weeks Sucuri have been tracking a new Malware threat that has gained significant traction over the past forty eight-seventy two hours. The malware they call the “Active VisitorTracker Campaign” is fairly easy to identify because of very particular “visitorTracker_isMob” code being used.

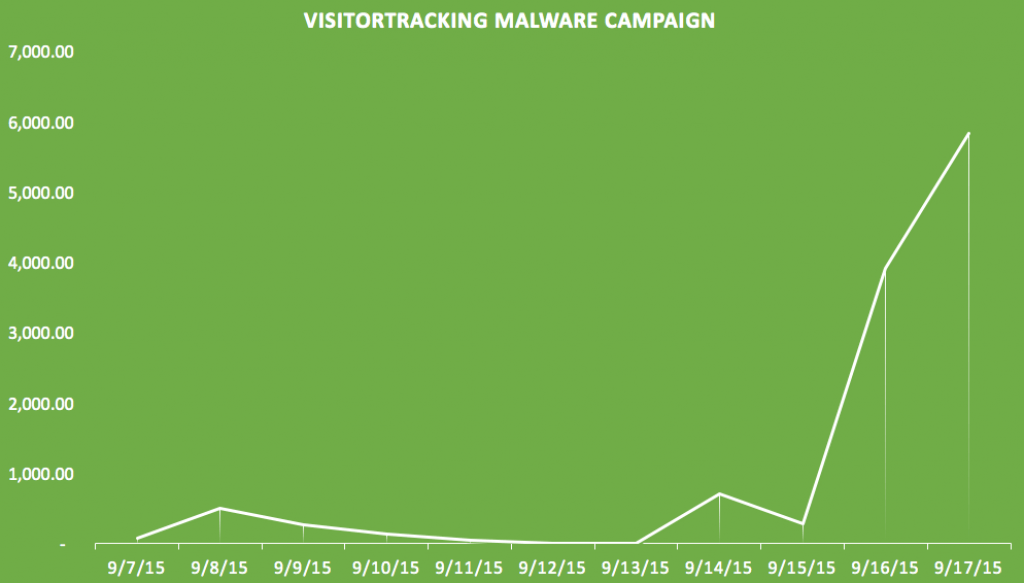
As of the 18th September 2015, slightly over 6 million web sites now contaminated, with over 5 million of these infections occurring within the last 48 hours. The chart created by Sucuri shows the rate of infections below:

Malware rising trend by Sucuri
See the rise especially 15th September onwards – Source: Sucuri

What does the Active VisitorTracker Malware do?

Based on Sucuri, the final objective of the infection is to redirect the visitors of the website to a Nuclear Exploit Kit landing pages, which may in turn use numerous methods to infect the physical computers of these visitors. Some examples of the strategies used include infecting the visitors computer utilizing Flash, Silverlight, PDF, and Internet Explorer to install malware or ransomware.

For more detailed \ technical article on the Nuclear Exploit Kit click here.

The exploit works by inserting the following code in to your web site:

  • function visitorTracker_isMob( ) var ua = window.navigator.userAgent.toLowerCase(); if(/(androidmobile|avantgo|bada\/|blackberry|blazer|compal|elaine|fennec|hiptop|iemobile|ip(hone|od)|iris|kindle|lge |maemo|mi..|v400|v750|veri|vi(rg|te)|vk(40|5[0-3]|\-v)|vm40|voda|vulc .. |vx(52|53|60|61|70|80|81|83|85|98)|w3c(\-| )|webc|whit|wi(g |nc|nw)|wmlb|wonu|x700|yas\-|your|zeto|zte\-/i.test(ua.substr(0,4))) return true; return false; /* .. visitorTracker .. */ /*

This code will then force the visitors web page to load an iframe from one of many Nuclear Exploit Kit landing pages which then infects the visitors computer system.

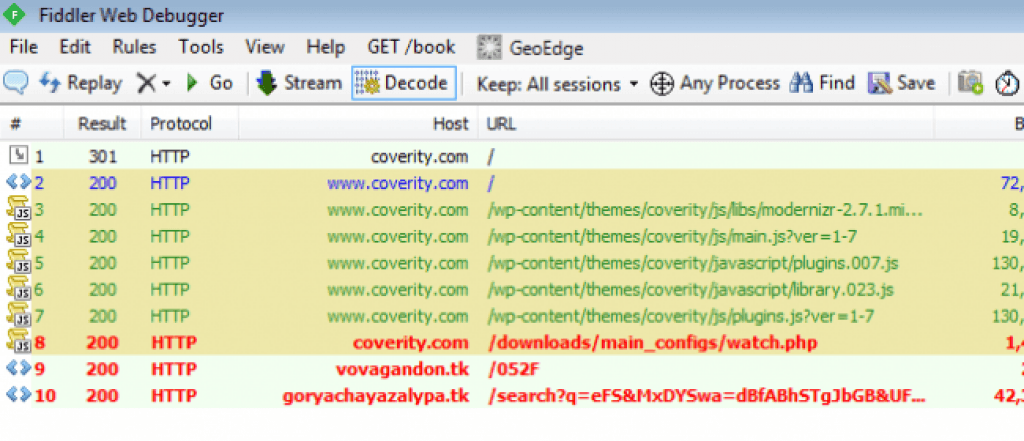
An example of the exploit in action has been noted by Jerome Segura from MalwareBytes showing an infection on a web site owned by a big security provider (Coverity):

Security site effected
Source: Malwarebytes

However they aren’t the only major security firm affected by this exploit.

Sucuri itself is infected by this Malware [Update: FALSE POSTIVE]

What concerns us very deeply is that Sucuri’s own labs (dot) sucuri (dot) net (don’t visit it – we are going to update when it’s secure) website is contaminated by this very malware. Their main blog post on this very Malware links to an article on that sub-domain with additional information on the exploit.

For a security firm, it’s quite serious that they’re really directing you to click a link to a contaminated page, and we immediately reached out to them via their support site and via their live chat to let them know. At the present time we do not have a reply/see any action has been taken.

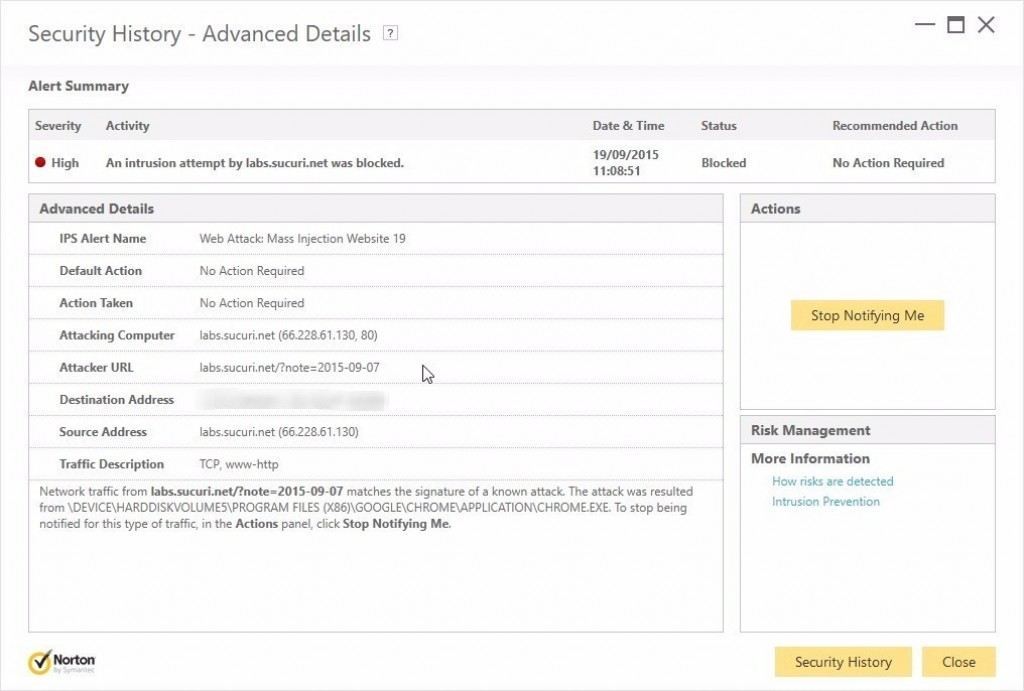
We were first alerted to the fact their website was infected by Norton Antivirus as shown beneath:

Norton says Sucuri infected
Norton says Sucuri is infected with the malware

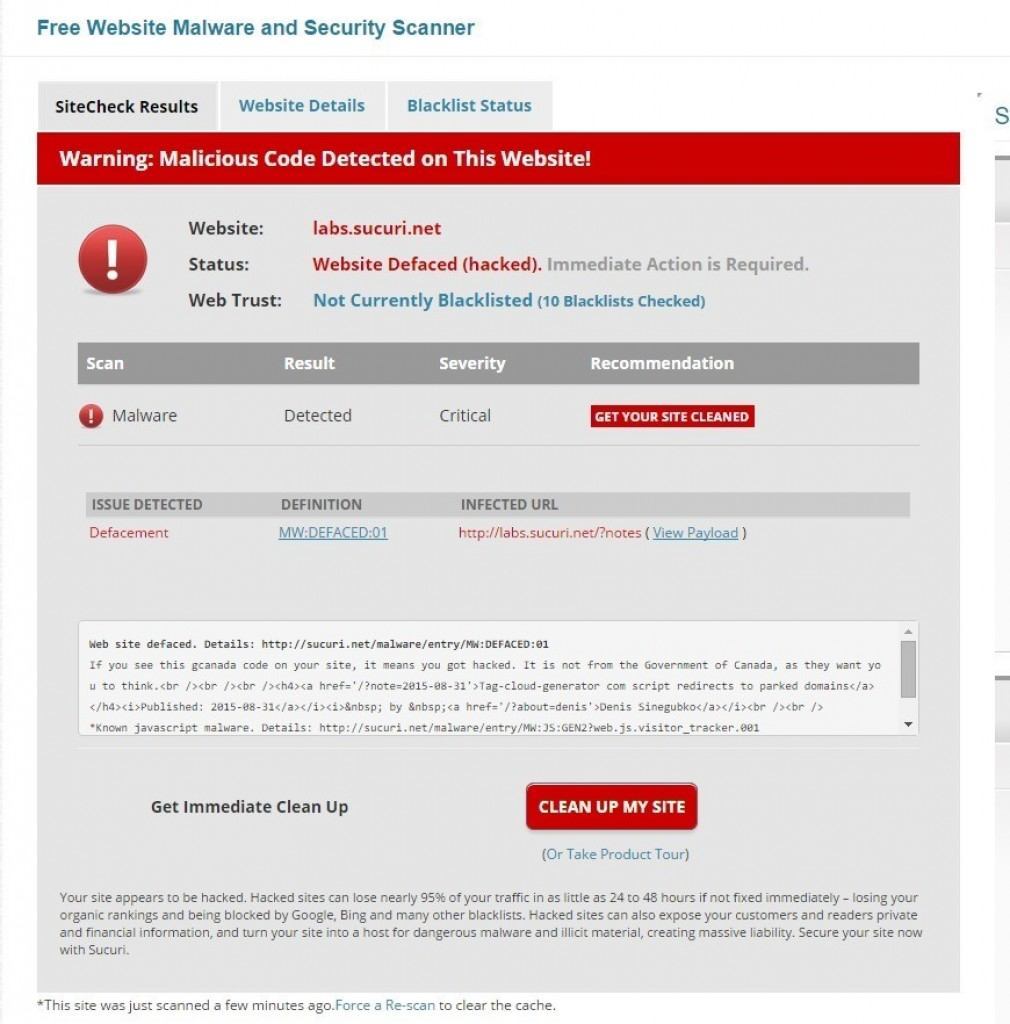
We then followed this up by using Sucuri’s own Site Scanner Tool, which confirmed that malicious code was detected, and that the code of the infection contained the following:

  • if(visitorTracker_isMob())

while also referring to their Malware entry: MW:JS:GEN2 (we will link to the page once we confirm the malware has been eliminated).

You can see a screenshot of their infection below:

Sucuri Infected - Checked by Sucuri
Source: Sucuri

Obviously, it is extremely serious that a web site people use to find out extra info on this infection is in turn responsible for spreading the infection itself.

UPDATE:

SUCURI REPONDED: “Indeed, since we publish details about attacks and malicious code on labs.sucuri.net, this can sometimes be flagged in SiteCheck. Not a big deal, though — you can see it’s alerting about a blog post that actually discusses the malware in question.

THE CEO of SUCURI then Added:

Yes, we flagged ourselves. and it caused others, like Norton to flag us as well.. these however are false positives. We have direct lines of communication with many vendors

Many of Infected Sites already blacklisted by Google

The seriousness of this Malware cannot be understated. Not only are you opening up your Guests computers to malware/ransomware, but Google appears to be very quickly blacklisting any site affected by this exploit.

Based on Sucuri, 17% of all websites they’ve found with the exploit are already blacklisted by Google and other popular blacklists.

How to test if your Site is infected with the VisitorTracker Malware?

The simplest method to check if your website is contaminated is to use this free tool by Sucuri. (This is safe to use)

How can you protect yourself as a website visitor?

While we haven’t checked all firewalls or antivirus programs but we are able to confirm that MalwareBytes and Norton successfully prevented us from visiting a website infected with this malware.


Here is Mr Tony Perez’s (CEO of Sucuri) full response. We (GadgTecs) apologize deeply for the confusion.

Thanks for sharing our information, but I did want to let you know it is a bit misleading. We are not and have not been compromised by this infection.

As an organization we invest heavily in research, specifically the public disclosure of that research to keep communities such as this one informed. This sometimes requires us to release snippets of malware variants, such as was the case here.

Yes, we flagged ourselves.. 🙁 and it caused others, like Norton to flag us as well.. these however are false positives. We have direct lines of communication with many vendors

If you have any other questions, please let me know I’d be happy to expand on the subject if required.

Tony Perez
Sucuri – CEO

tony@sucuri.net